Why WordPress Plugin Ads Keep Returning After You Dismiss Them
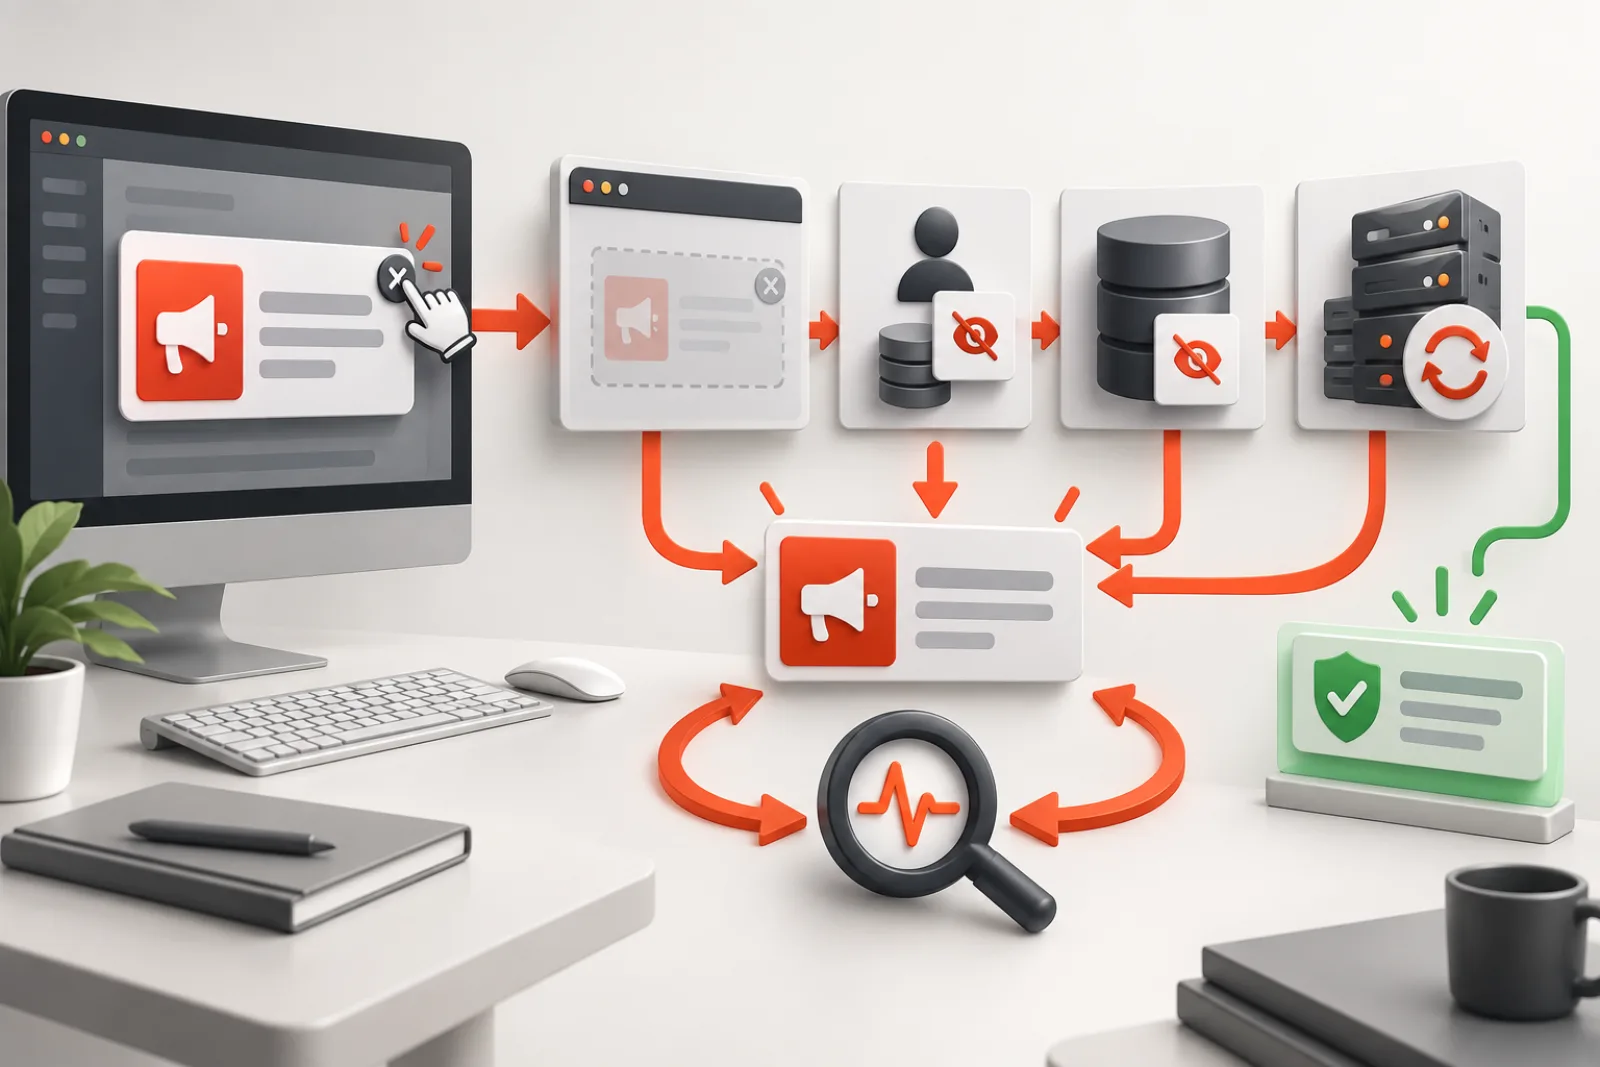
A WordPress plugin ad usually returns because the close button hid one rendered element but did not create a durable dismissal that the plugin recognizes. Some notices intentionally dismiss only for the current screen; others save state per user, per site, across a Multisite network, in a cookie, or through an AJAX request. If that persistence fails—or the plugin changes the campaign identifier—the banner is rendered again.
First determine what “dismiss” means
WordPress adds client-side behavior to notices marked is-dismissible, but the official admin_notices documentation warns that this applies only to the current screen. It does not automatically stop the notice from appearing after a reload or on another page. A plugin must implement and validate its own persistent state when it promises “don’t show again.”
| Behavior | Likely mechanism | Evidence to check |
|---|---|---|
| Returns immediately after reload | Visual close only or failed save | Network request and console error |
| Returns in another browser | Cookie/local browser storage | Stored browser state |
| Returns for another administrator | Per-user preference | User-meta scope |
| Returns on another site in Multisite | Per-site option | Site versus network setting |
| Returns after plugin update | Campaign/version key changed | Changelog and stored dismissal ID |
| Appears seconds after page load | Late JavaScript or remote campaign | DOM/network timeline |
Capture the source before hiding it
Record the notice text, screen URL, plugin branding, HTML classes/IDs, close-button behavior and time of appearance. In the browser Network panel, enable “Preserve log,” dismiss once and look for a request to admin-ajax.php or a REST endpoint. Save its status and sanitized response. Do not publish cookies, nonces or account identifiers.
If there is no network request and no storage change, the close control may only remove the element. If a request returns 403, the session, nonce, WAF or capability check may have rejected it. A 200 response does not prove the plugin stored the state; inspect the response and re-test after reload.
Find whether dismissal is per user or per site
Test with a second administrator on staging. If the banner remains hidden only for the first account, the plugin likely uses user meta. That is often correct for onboarding, but poor for a site-wide commercial campaign if every agency user must dismiss it. If all accounts share state, check site options. In Multisite, repeat on another subsite and Network Admin because network options and site options have different reach.
Watch for cache interference
Authenticated admin pages and personalized AJAX responses should not be served from a shared page cache. A reverse proxy or CDN that ignores cookies can replay an older notice or an expired nonce. Object-cache failures can also prevent the saved option from persisting. Purge only after identifying the cache layer, then verify that one dismissal survives across fresh requests without exposing one user’s state to another.
Understand campaign identifiers
A well-designed plugin stores a specific notice or campaign ID rather than a single forever flag. That allows genuinely new security or migration notices to appear. It also means a vendor can change the ID on every release and unintentionally resurrect the same promotion. Compare markup and stored keys before and after an update. Report repeat promotions with precise version evidence.
Do not hide by color or generic class
Selectors such as .notice, .notice-warning or every dismissible notice are too broad. Security warnings, failed backup alerts, payment configuration errors and database migration messages may use the same presentation classes as marketing. Classify the message by source and purpose, then target a stable callback, widget ID, menu slug or narrow signature.
A safe diagnostic workflow
- Back up and reproduce on staging where possible.
- Record the exact notice and owning plugin/version.
- Dismiss with developer tools open.
- Check request, response and browser storage.
- Test reload, another screen, another user and—if applicable—another subsite.
- Inspect cache/WAF logs for rejected persistence.
- Confirm whether an update changes the campaign ID.
- Ask the vendor for a supported opt-out when the behavior is defective.
- Only then create a narrowly scoped suppression rule.
Worked example
An agency dismisses a rating banner, but it returns for every client editor. The close request succeeds and writes user meta for the administrator who clicked it. The plugin is behaving as coded, but the scope conflicts with the agency’s policy. Instead of training every client, the agency preserves operational notices and suppresses only that known promotional callback for client roles. Administrators retain access to plugin settings and update warnings.
Classify notice purpose before persistence
Record whether the message is a security failure, migration requirement, configuration warning, license state, onboarding step, review prompt, discount or cross-sell. The same dismiss behavior can be appropriate for a rating request and dangerous for a failed backup. Purpose controls who may suppress it and for how long.
Keep uncertain notices visible to administrators until an accountable owner classifies them.
Trace the close control end to end
Inspect the click handler, request endpoint, status, response and subsequent storage change. Determine whether the element disappears before the server confirms persistence. If the request fails, the UI should not pretend the choice was saved.
Re-test after reload, new session and cache expiry. Preserve sanitized evidence for the vendor.
Audit user-meta persistence
When dismissal is per user, confirm the correct user ID, meta key, value and campaign identifier change. Test an administrator and client role. Repeated writes can fail because of capability checks, nonce expiry, custom authentication or object-cache problems.
Do not copy one user’s preference into every account without a documented site-wide policy.
Audit site and network options
In Multisite, distinguish site options from network options. A subsite dismissal may correctly leave the Network Admin banner visible, while a network policy may intentionally apply to every site. Record blog and network scope with the decision.
Avoid a global database replacement of similarly named keys. Use the owning plugin’s supported setting or API.
Check cookies and local storage
Browser-only persistence will not follow a user to another device and may disappear under privacy cleanup. Inspect cookie domain, path, secure attributes and expiry, or the specific local-storage key. A migration from www to the apex host can make an old cookie irrelevant.
Do not weaken cookie security merely to persist a promotion choice. Prefer authenticated server state when the decision should follow the user.
Investigate WAF and REST rejection
A dismissal request may match a security rule, arrive without the expected nonce or use a REST route hidden from one role. Capture status, response and rule ID. Create only a narrow exception after confirming the request is authorized and validated.
Test an unauthorized request afterward. Suppression convenience must not create a writable unauthenticated preference endpoint.
Understand transient and time-based campaigns
Some plugins intentionally suppress a notice until a timestamp, next version or campaign period rather than forever. Inspect documented behavior before calling it broken. A recurring security renewal reminder may be justified; a weekly repeated upsell may violate agency policy.
Record the intended recurrence and review date. Do not create permanent suppression for operational deadlines.
Handle renamed campaign IDs
Compare the rendered notice ID and stored dismissal before and after updates. Vendors may version a campaign to show new information, but minor wording changes should not resurrect the same promotion indefinitely. Report the precise identifiers and releases.
If a local rule targets an identifier, treat plugin updates as a regression trigger and verify that critical new notices still appear.
Preserve accessible dismissal behavior
The close control needs an accessible name, keyboard operation and visible focus. Removing a banner visually while leaving a link or button focusable creates a confusing hidden stop. A server-rendered suppression should omit the promotional component entirely for the intended scope.
Test with keyboard and a screen reader for both client and administrator roles.
Prefer vendor controls and documented filters
Look for a plugin setting, account preference, filter or supported constant before intercepting markup. A vendor control is more likely to survive updates and can stop related network work. Document where the choice is stored and how to restore it.
If no supported opt-out exists, send evidence and request one. Keep local suppression minimal.
Build a role-based admin policy
Clients may need operational errors and task guidance but not rating prompts or upgrade sales. Site administrators may need license and update information. Network operators may require fleet-wide failure alerts. Write this policy before implementing rules.
Use capability-aware scope, not usernames. Test newly created roles and administrators who were not present when the rule was added.
Use narrow suppression evidence
Target a stable callback, widget ID, menu slug, script handle or verified campaign signature. Combine source and purpose when one signal is ambiguous. Avoid generic words such as “upgrade” alone because a database upgrade warning can be critical.
Keep an allowlist for known operational messages and stop suppression when classification confidence falls.
Worked case: successful AJAX, failed object cache
A close request returns success and updates an option, but the next request reads a stale cached value from a broken persistent cache. The banner returns, so staff repeatedly click it. The team verifies database and cache divergence, repairs invalidation and confirms fresh requests read the new option.
Adding CSS would have hidden the evidence and left other settings inconsistent.
Worked case: update creates a new campaign ID
A plugin release changes review_prompt_v2 to review_prompt_v3 without meaningful content change. Every user sees the rating request again. The agency documents versions and requests a supported site-wide opt-out.
Until then, a role-scoped rule targets that plugin’s known review callback while update and security notices remain visible.
Run a post-update regression
After major plugin changes, visit dashboard, plugin page, update screen and relevant settings with client and administrator roles. Wait for late scripts, reload and test dismissal persistence. Verify menu, toolbar and footer surfaces as well as standard notices.
Record new or changed identifiers. Remove obsolete rules so they do not accidentally match future components.
Definition of done
The exact source, persistence mechanism and scope are known; the promotion remains absent through reload, session, device and relevant role tests according to policy. Critical notices remain visible and actionable, hidden controls leave no accessibility residue, no required background function is disabled, and update regression plus rollback are documented.
Distinguish hiding from stopping the source
CSS or DOM removal changes presentation while the plugin may still render markup, make remote requests, allocate scripts or write analytics. Inspect network and server behavior after suppression. When a vendor setting or callback removal can prevent the promotional component safely, it is cleaner than hiding pixels.
Keep functional license and update checks if administrators depend on them.
Audit remote campaign services
Some banners arrive from a vendor API and vary by account, date or product. Record the destination, cache, timeout and privacy impact. Do not block a whole vendor domain if it also serves update metadata, documentation or licensing.
Ask for a supported promotions opt-out and verify the editor remains responsive during vendor outages.
Check page builders and custom admin screens
Promotions may be injected into Elementor, WooCommerce or plugin-specific applications rather than standard notice hooks. Capture the owning script, component or endpoint. A general wp-admin rule may miss these screens or break their application layout.
Test load, save and support paths after any targeted removal.
Preserve update and license operations
An upgrade banner, expired-license warning and update authorization can share branding. Suppressing the sales CTA must not block access to changelogs, vulnerability fixes or license renewal needed for updates. Classify controls and destinations individually.
Verify plugin list, update screen and settings for administrator roles after policy changes.
Handle notices that appear only after actions
Import, save, activation or migration may produce a notice using the same wrapper as a promotion. Test success and failure states, not just dashboard load. Preserve messages that explain partial completion, rollback or data risk.
A keyword rule should never discard an error merely because it also contains “upgrade” or “premium.”
Maintain a suppression registry
Record plugin, version, surface, callback or identifier, purpose, target roles, technique, approver, date and rollback. Include screenshots and expected retained warnings. Remove stale entries after the plugin provides a native opt-out or the campaign disappears.
This registry turns scattered snippets into an auditable dashboard policy.
Test newly created users
Onboarding prompts may depend on account age or missing user meta. A rule tested only with a long-lived administrator can miss what every new client sees. Create a staging user with the intended role and walk through first login, dashboard, editor and plugin pages.
Confirm essential onboarding remains available through documentation or a purposeful dashboard module.
Review mobile and narrow admin layouts
Notices can cover controls or create horizontal overflow on smaller screens. Test dismissal and suppression at common tablet widths. Hidden banners must not leave blank regions, inaccessible close buttons or shifted focus order.
Do not use viewport-specific CSS as the only policy; source classification should remain consistent.
Monitor for recurrence without storing content
Count known promotional source matches and unknown admin surfaces by plugin/version. Alert when a rule stops matching or a new repeated campaign appears. Avoid logging full notice bodies when they may contain account, path or license details.
Review unknowns manually before expanding heuristics. A sudden new warning could be operationally important.
Build a vendor escalation package
Provide plugin version, notice text with secrets removed, screen, user scope, campaign ID, dismissal request status, storage mechanism and reproduction after reload. State whether a native setting exists and why the current scope conflicts with agency needs.
Request a durable, accessible, site- or role-aware opt-out rather than relying indefinitely on markup scraping.
Audit database cleanup and resets
Optimization or privacy jobs can remove plugin options and user meta they mistake for stale data. Correlate recurrence with cleanup schedules, resets and staging-to-production synchronization. Exclude active dismissal keys only after confirming ownership and retention need.
Do not restore an entire old options table to recover one preference; use scoped backup evidence and the plugin API.
Check activation and deactivation behavior
A plugin may delete dismissal state on deactivation or recreate campaigns on activation. Reproduce during staged lifecycle testing and inspect documented uninstall policy. Updating should not behave like a clean install unless the vendor explicitly migrates state that way.
Preserve settings backups before troubleshooting through deactivation, especially on sites with licenses and integrations.
Review staging and cloning effects
Cloning a site can copy user or site dismissal state, while production deployment may overwrite it from staging. Decide whether promotional preferences are environment-specific and exclude them from one-way content sync when appropriate.
Never copy production secrets or personal user meta into an insecure staging environment merely to reproduce a banner.
Handle role changes and user switching
A client promoted to administrator may legitimately see operational license and update notices previously suppressed. Re-evaluate policy by capability at request time rather than storing one permanent visibility flag from the old role.
Test user-switching and impersonation tools carefully so one account’s dismissal does not mutate another user’s meta.
Check analytics and tracking behavior
Promotional components may send impression or click events even after visual hiding if their scripts still run. Inspect network activity and privacy disclosures. Stop unnecessary marketing scripts on suppressed admin surfaces through supported controls where possible.
Do not block telemetry required for security or update delivery without understanding its purpose and policy.
Create a client-facing admin standard
Document which warning classes clients always see, which operator notices route to the agency and which marketing surfaces are removed. Give clients a support path for missing features or unexpected banners. The goal is clarity, not a silent dashboard.
Review the standard with onboarding, maintenance and incident teams so responsibilities match actual access.
Report outcomes beyond visual cleanliness
Measure repeated promotions removed, operational warnings preserved, unknown notices reviewed, client support questions and admin load changes. Record false positives and update-rule failures. A dashboard with fewer pixels is not successful if license expiry or backups become invisible.
Keep evidence by plugin version and role so the policy remains maintainable.
Set a review date for every exception
A temporary campaign rule should not become permanent infrastructure. Review it after the vendor adds an opt-out, changes markup or ends the promotion. Confirm the rule still targets only the intended component and remove it when no longer necessary.
During review, retest critical notices and newly created users. This catches both silent rule failure and a broadened heuristic before clients lose important operational information.
Verify a complete administrator journey
Test first login, dashboard, plugin list, update page, settings, content editing and logout under the intended roles. Confirm the promotion follows policy at every surface while security, backup, payment, migration and compatibility messages remain visible. Wait for late scripts and repeat after a fresh session.
Record the final source and scope, not just a screenshot of a clean dashboard. That evidence lets a future maintainer distinguish deliberate suppression from a broken notice system.
How MeNoAds helps
MeNoAds provides separately switchable controls for promotional admin notices, dashboard widgets, footer text, meta boxes, menu items, toolbar nodes, plugin-page banners, update-page promotions and JavaScript-injected notices. Its notice layer recognizes known promotional callbacks and keyword patterns rather than relying on one generic CSS rule.
Its limitation is the same classification problem: plugin markup and callbacks change, and promotional-looking notices can contain required setup or security information. Test the current installed version on staging, keep administrators’ operational visibility, and review what was removed after major plugin updates.
Verification checklist
- The promotion stays absent across reloads and relevant screens.
- Critical error, security, update and backup notices remain visible.
- Client and administrator roles see the intended different surfaces.
- Multisite scope matches site or network policy.
- No dismissal endpoint returns an error.
- Plugin settings, updates and support paths still work.
- The rule is documented with owner, reason and review date.
Related WPStack guides
Frequently asked questions
Why does WordPress’s X button not remember dismissal?
The standard dismissible class can remove a notice only on the current screen. Persistent dismissal must be implemented by the plugin.
Where do plugins store dismissals?
Common locations include user meta, site options, network options, cookies or local storage. Inspect the actual request and scope rather than guessing.
Why did a plugin update bring the ad back?
The campaign identifier or stored setting may have changed or been reset. Compare versions and report repeat campaigns to the vendor.
Can I hide all .notice elements?
That is unsafe because critical operational warnings use the same notice system. Target known promotional sources narrowly.
Does suppressing a banner stop its background requests?
Not necessarily. CSS hiding changes presentation only. Removing a callback may prevent rendering, while late scripts or remote calls require separate evidence.
References
Aditya Bhimrajka is a technology entrepreneur, product strategist, and software solutions expert with over a decade of experience building scalable web and mobile applications. His expertise spans SaaS, AI, cloud technologies, custom software development, and digital transformation. Passionate about solving real-world business challenges through technology, Aditya shares practical insights on WordPress, plugins, software development, startup growth, product strategy, and emerging technologies. At WPStack, he writes actionable, experience-driven content that helps developers, businesses, and website owners build secure, high-performing, and future-ready WordPress solutions.