
How to Remove JavaScript-Injected WordPress Admin Notices Safely
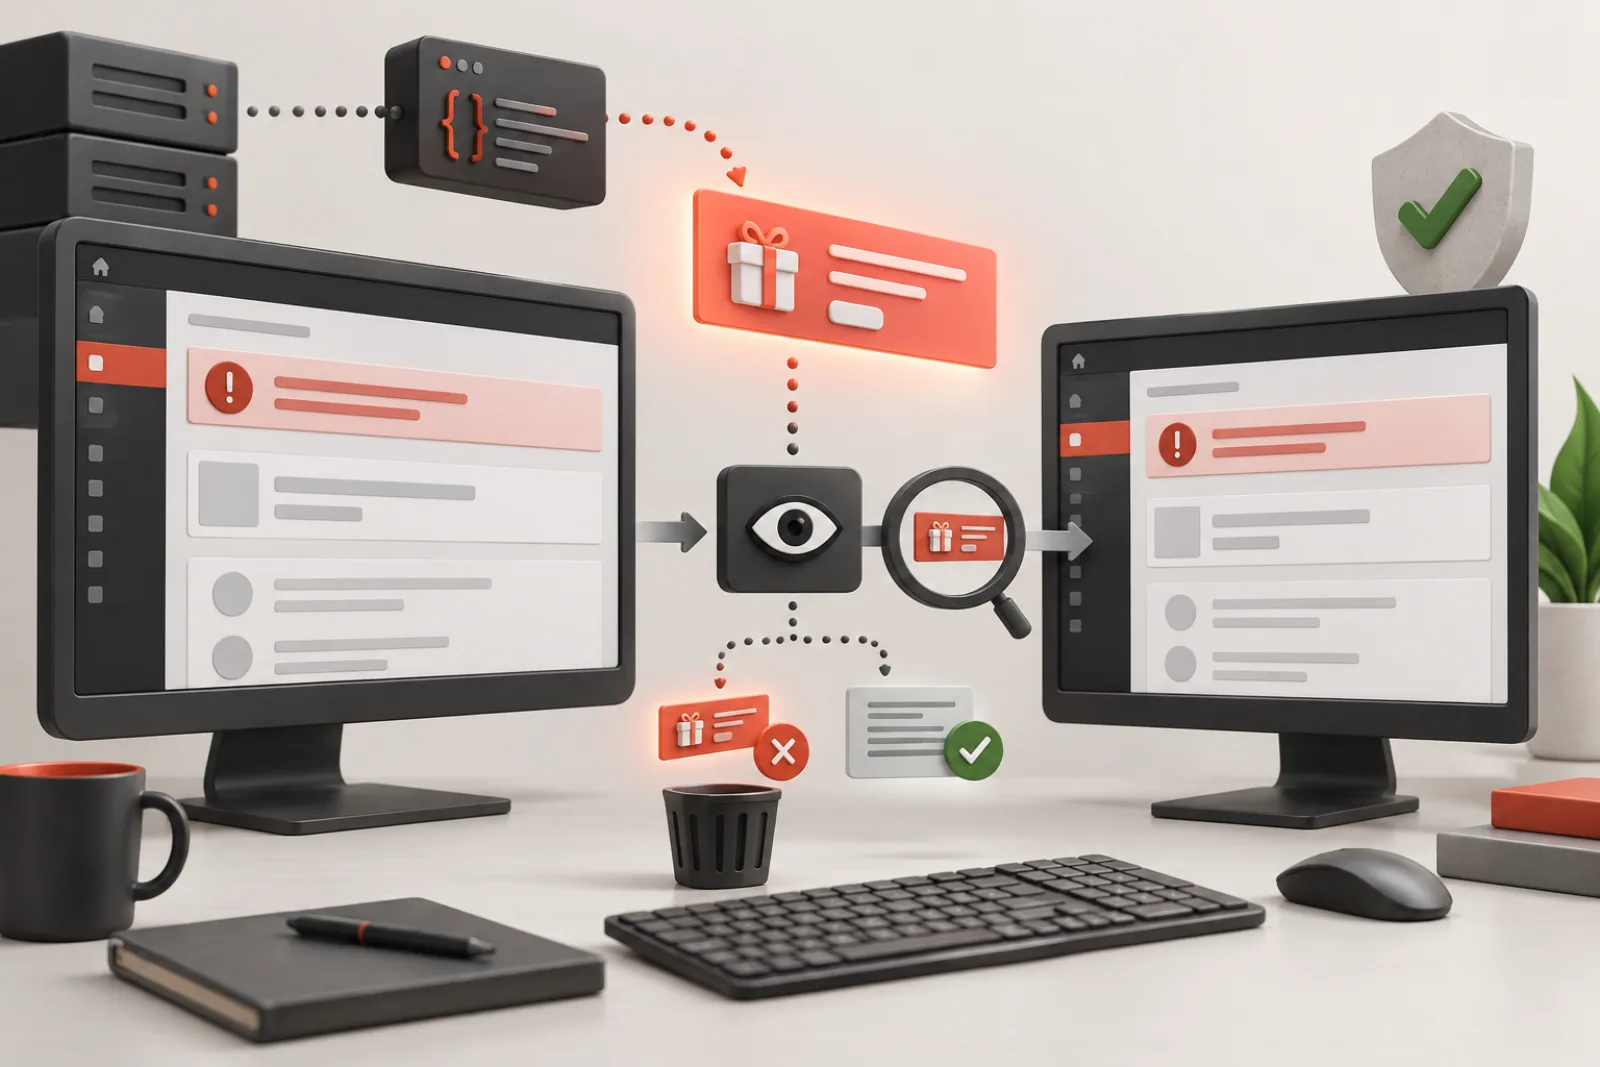
To remove a JavaScript-injected WordPress admin notice safely, identify the script and message purpose before observing the DOM. A late banner does not pass through the normal PHP notice hooks, so server-side callback removal may never see it. The safest order is vendor opt-out, screen-scoped script prevention, narrow DOM removal, then regression testing that critical alerts remain.
Prove the notice is injected late
Reload with browser developer tools open. Compare initial page source with the live Elements tree and preserve the Network log. If the banner is absent from the response but appears after a script or API call, record the added node, timestamp, script initiator, request endpoint and owning plugin. Redact cookies, nonces and personal data.
| Finding | Preferred response |
|---|---|
| Vendor setting disables campaigns | Use the supported setting |
| Promo script is separately enqueued | Prevent that handle on scoped screens |
| Shared script provides critical functions too | Do not dequeue; target only the promo node |
| Remote response mixes operations and marketing | Ask vendor for separation; avoid response tampering |
| Stable promo signature, no opt-out | Use a narrow observer with tests |
| Message purpose is uncertain | Retain and escalate for classification |
Prefer source prevention to cleanup
WordPress recommends enqueuing admin scripts through admin_enqueue_scripts and scoping them to the pages where needed. If a plugin exposes a campaign setting or filter, use it. If it registers a distinct promotional script handle, a small integration can dequeue that handle only for approved roles and screens—provided the handle has no functional responsibilities.
Do not block all requests to a vendor domain. The same origin may provide license checks, updates, security feeds or required APIs. Classify by exact script/endpoint and business function.
Why CSS is insufficient
display:none can leave the script, network call and DOM work intact. A hidden banner may contain focusable links or duplicate IDs and can briefly flash before styles apply. Broad attribute or text selectors can also hide operational notices. CSS may be an emergency visual mitigation, but it is not a complete or robust control.
Design a narrow MutationObserver
When late insertion cannot be prevented safely, observe the smallest stable container, not the entire document forever. Inspect only added nodes, match a strong combination of plugin-owned class/data attribute and known promotional signature, remove the specific banner, then disconnect when the expected lifecycle is complete. Avoid scanning all text on every mutation.
Text can be translated or changed by campaigns, so it is a weak sole identifier. Generic words such as “upgrade,” “important” or “license” can occur in legitimate warnings. Treat a stable vendor namespace plus a precise component signature as stronger evidence.
Preserve accessibility and critical alerts
Test with keyboard navigation and an accessibility tree. Removing a node is better than visually hiding an interactive advertisement, but the rule must not remove adjacent live regions or alert containers. Maintain fixtures for a failed backup, vulnerable plugin, payment problem and database migration. Those should render even when promotional filtering is active.
Scope by screen and role
A campaign may be acceptable on its own plugin page for an administrator but distracting on every post editor screen for a client. Use current screen IDs and capabilities to scope behavior. Role labels alone are less reliable than capabilities, especially with custom roles. In Multisite, test site admin and Network Admin separately.
Measure performance consequences
A poorly implemented observer can create more admin lag than the banner it removes. Record observer callback count and execution time during navigation, typing, media modals and builder sessions. The filter should do near-zero work when no matching node arrives. If the removed component’s script continues polling the network, solve that separately or document the remaining cost.
Worked example
A promotion appears two seconds after every edit screen loads. The notice is not in HTML and no PHP notice callback owns it. A plugin script fetches campaign JSON, but that same bundle also renders a required license-expiration warning. Dequeuing it is unsafe. The agency implements a screen- and role-scoped observer matching the vendor data attribute and campaign component, removes only upsell nodes, and keeps license warnings. Performance tracing shows negligible observer work, and notice fixtures pass.
Capture the mutation timeline
Preserve the network log, reload once and record when the node appears relative to DOM ready and later requests. Use developer tools to inspect the added subtree and the script or callback that created it. The earliest initiating request is more useful than the final CSS class.
Redact account, license and nonce values before sharing evidence.
Find the source script and handle
Trace the script URL to a plugin, theme, remote campaign service or browser extension. In WordPress, identify the registered handle, dependencies and screens where it is enqueued. The same bundle may power both settings and promotion, so do not dequeue it until functions are mapped.
Prefer a vendor setting or filter that disables only announcements.
Inspect remote campaign requests
Record destination, request purpose, timing, failure behavior and response fields. Blocking the host may also disable licenses, updates or documentation. If the campaign is unnecessary for client roles, request a supported opt-out or prevent only the promotional component from rendering.
Review privacy and avoid sending client identifiers without a valid need.
Choose source prevention when possible
Use a documented plugin option, account preference, filter, feature flag or screen-specific enqueue condition. Source prevention avoids extra network, parsing, DOM and accessibility cost. Confirm settings, validation and operational warnings continue to function.
Keep the exact plugin version and rollback because vendor APIs can change.
Design a stable DOM signature
When observation is unavoidable, combine plugin-owned IDs, data attributes, links and container relationships. Do not match generic classes or words alone. Require enough evidence that a security warning with similar styling cannot be removed.
Maintain an allowlist for critical surfaces and log unknown candidates for review without storing sensitive text.
Scope the observer tightly
Observe the smallest stable parent and only the child-list mutations needed. Exit early on irrelevant screens and roles. Disconnect after the known element is handled if it cannot return. Avoid watching the entire document subtree indefinitely.
Measure callback count and execution time on complex admin applications.
Handle single-page admin navigation
Plugin dashboards may change routes without a full page load and recreate campaigns. Test tab changes, modal opens, save results and back navigation. A one-time page-load cleanup may fail, while a broad permanent observer can become expensive.
Use the application’s supported extension point or a narrowly bounded route listener when available.
Preserve accessibility
Remove the complete known component, including focusable links, close buttons, live-region announcements and overlays. Confirm focus does not jump to nowhere. Do not use visual opacity or off-screen positioning that leaves content in the accessibility tree.
Test keyboard and screen reader in both the suppressed and retained critical-notice states.
Protect security and failure messages
Late JavaScript can also report failed saves, expired sessions, payment errors and scan results. Build fixtures for these conditions. A keyword such as “upgrade” can appear in a database upgrade requirement and must not become a blanket rule.
When classification confidence is uncertain, show the notice to administrators.
Review Content Security Policy implications
Do not weaken CSP to permit an unneeded remote campaign script. Conversely, a policy violation that blocks a required settings application should be fixed with precise trusted sources, not hidden as a promotion issue. Use report-only testing where appropriate.
Retain clickjacking and script protections after changes.
Test browser extensions as an alternate source
If the banner appears in one profile only, use a clean supported browser. Password managers, security tools and vendor extensions can inject DOM into wp-admin. A site code change cannot reliably remove an extension-owned surface for every user.
Coordinate a scoped admin-site exception with the extension owner if policy permits.
Audit background requests after visual removal
Compare network, CPU and console activity. DOM deletion may not stop timers, fetches or event listeners. Source prevention can provide real savings; presentation cleanup may provide none. State claims by measured layer.
Keep required update and security requests even if they share vendor branding.
Use role and screen policy
Clients may have promotions suppressed while administrators retain license and support information. Evaluate capabilities at runtime and exact screen IDs. Do not store a single global flag that removes required network notices.
Test newly created users, multisite and Network Admin separately.
Build a regression fixture set
Include a known late promotion, server-rendered notice, AJAX save failure, session warning, update error and plugin application modal. Verify expected visibility, keyboard focus and network requests. Run after plugin, theme and WordPress releases.
Remove fixture data after testing and keep sanitized results.
Worked case: observer removes a payment error
An agency observer deletes every late element containing a CTA button. A WooCommerce payment failure injects a notice with a “Review settings” button and is removed too. Orders begin failing without a visible explanation.
The team rolls back, builds a source-based policy and targets only a known campaign component. Payment-error fixtures become mandatory regression tests.
Worked case: source prevention removes network cost
A plugin setting disables product announcements. Before the change, a remote campaign request and large bundle run on every dashboard. Enabling the supported opt-out removes both, while settings and updates still work.
The team deletes its observer and records the native control as the maintained solution.
Definition of done
The source, timing and purpose are proven; the narrowest supported prevention or bounded observer is used; client and administrator scopes match policy; critical dynamic errors remain visible; focus and accessibility are intact; unnecessary network or execution work is measured; and plugin-update regression plus rollback are documented.
Inspect event listeners and timers
Removing a node does not automatically detach listeners held elsewhere or stop intervals. Use a staging performance trace to see whether the campaign continues polling or observing. Source prevention is preferable when it avoids execution safely.
If an observer is retained, disconnect it when its bounded job finishes and verify no console errors follow.
Handle shadow DOM and iframes
Some admin applications render isolated components inside a shadow root or iframe. A document-level selector may not see them, and crossing origins may be prohibited. Identify the owner and use its settings or API rather than bypassing browser boundaries.
Do not weaken framing or script security merely to remove marketing content.
Verify save and update workflows
Late notices often appear after configuration saves, imports or updates. Trigger success, validation error, network error and permission denial. Confirm useful feedback remains and focus moves to the right status.
A suppression that leaves users uncertain whether a save completed creates more risk than the original clutter.
Test plugin application routes
Navigate every internal tab without full reload, open modals and return with browser history. Record whether the campaign is recreated and whether the observer cost grows. Avoid registering a new observer on every route transition.
Prefer one lifecycle-aware integration with cleanup.
Validate localization
Text-based signatures can fail in translated wp-admin or match an operational warning in another language. Test priority locales and rely on stable plugin-owned identifiers. Native reviewers should classify ambiguous wording.
Keep unknown dynamic notices visible to administrators until reviewed.
Protect against markup drift
When a plugin changes class names or nesting, a narrow rule should fail safely by leaving the promotion visible—not broaden itself. Monitor unmatched known sources and schedule review. Never fall back automatically to every notice or CTA.
Version signatures and keep the old rule available for rollback only while its release remains supported.
Use a small automated check
On a staging fixture, wait for the known campaign, assert its expected treatment, then trigger a critical AJAX notice and assert it remains. Check focusable descendants and background request count. This single regression is more valuable than a large brittle screenshot suite.
Human review still decides whether the notice purpose was classified correctly.
Prepare incident rollback
If support reports missing warnings, disable the rule through an administrator-only switch, preserve the current DOM and identify the new source. Do not delete all suppression code or disable the owning operational plugin.
After correction, replay the critical fixture set before restoring the policy.
Document limitations
State which screens, plugins, languages and injection mechanisms are covered. Browser extensions, cross-origin frames and encrypted remote applications may be outside control. Unknown does not mean clean.
Give each unsupported surface an owner and manual review step.
Maintain the solution
Review after vendor, WordPress, security-policy and browser changes. Remove local observers when native opt-outs become available. Compare performance and accessibility periodically.
The best long-term solution prevents the known promotion at its supported source and leaves dynamic operational feedback untouched.
Audit framework portals and React roots
A notice may render through a portal outside the plugin’s visible root. Trace component ownership and route state before choosing a selector. Removing a parent React node directly can cause the framework to recreate it or throw reconciliation errors.
Prefer an application preference or feature gate; otherwise target a stable isolated container and test every route transition.
Preserve focus during asynchronous removal
If a component appears while the user is typing or navigating, removal must not steal focus or strand it on a detached button. Observe active element before the change and move focus only when necessary to a logical surviving location. Test with keyboard at slow network speeds.
A visually clean page that disrupts interaction fails the policy.
Handle repeated network retries
Remote campaign code may retry when its element is removed or request fails. Capture request count across several minutes and an offline simulation. Block only the optional campaign through supported configuration, or ensure the client stops retrying after a bounded failure.
Uncontrolled retries can slow wp-admin even when no banner is visible.
Separate consent and marketing surfaces
Some late banners request telemetry consent, legal acknowledgement or account authorization. Do not classify them as promotions from style alone. Read the consequence and data flow, then route the choice to an authorized administrator. Retain records required by policy.
Marketing opt-ins can be suppressed only when the organization has chosen the appropriate default lawfully.
Test error boundaries
When a removed component shares a JavaScript application, verify error boundaries, loading states and API failures. An unexpected null campaign field should not crash settings. Use a mocked response with promotion present, absent, malformed and slow.
Report application assumptions to the vendor instead of maintaining an expanding DOM patch.
Close with measurable evidence
Compare DOM nodes, focus order, script execution, remote requests, console errors and admin interaction time before and after. Confirm critical late notices still appear. Keep a sanitized trace and regression fixture keyed to plugin version.
Remove temporary debugging observers and document the chosen source-level or bounded fallback control.
Review mutation performance under real admin work
Open the block editor, Elementor, WooCommerce orders and the plugin’s own application while recording observer callbacks. Bulk DOM changes can make an apparently tiny selector expensive. The rule should exit immediately on unrelated screens and avoid repeated full-document queries.
Test a slow device and long session. If callback volume grows, disconnect duplicate observers and fix lifecycle registration.
Use an approval and exception record
Store the plugin, version, component signature, target roles, business classification, retained critical states, technique, tests and reviewer. If wording or markup changes, leave the new component visible until reclassified rather than broadening the matcher automatically.
Review the record during plugin updates and site handoff. Delete the local workaround when a supported vendor control exists.
Prepare a safe vendor report
Provide the route, time of injection, sanitized DOM signature, initiating script, campaign request and accessibility impact. Explain the desired role- or site-wide opt-out. Do not send cookies, nonces, license keys or customer content.
A precise report can produce a durable setting and eliminate fragile downstream observers for every customer.
Until a vendor fix ships, pin the local rule to the tested release range and fail open for unknown versions. Leaving a new promotion visible for administrator review is safer than applying an unverified selector to changed markup. Test the new release on staging, update the fixture and remove obsolete signatures once the rollout is complete.
Document whether the fallback removes only the node or also prevents its source request. This keeps performance claims accurate and tells future maintainers what remains to solve.
Before closing, repeat the test with a throttled connection and after application cache expiry. Delayed campaigns sometimes arrive outside the initial window. Verify the rule still handles only the approved promotion, disconnects cleanly, creates no console errors and leaves asynchronous save, security and payment feedback intact. Store the result with exact application and browser versions.
Test browser zoom, reduced motion and a screen reader because late removal can interact with animation and live regions. If the campaign announces before deletion, source prevention is required to prevent noise; deleting the node afterward is too late for assistive technology. Confirm no overlay or body-scroll lock remains.
Finally, review admin source maps and logs only in protected environments. DOM snapshots and responses can contain account, license or customer data. Share a sanitized reproduction with vendors and delete temporary captures according to the site’s retention policy.
How MeNoAds helps
MeNoAds includes a separately controlled JavaScript notice observer alongside its server-side notice and admin-surface blockers. Its implementation targets known promotional patterns after page load, which addresses banners that bypass standard PHP notice actions.
That remains heuristic: third-party DOM structures and wording change, and not every late notice is an advertisement. Keep the observer optional, test it after plugin updates, and disable the specific blocker immediately if it obscures required functionality.
Regression checklist
- The owning script and insertion timing are documented.
- A vendor setting/filter was checked first.
- Any dequeue is screen- and role-scoped and functionally safe.
- The observer watches the smallest viable container.
- Matching uses stable source evidence, not generic text alone.
- Keyboard and accessibility-tree checks pass.
- Critical notice fixtures remain visible.
- Observer time and remaining background requests are measured.
- Rules are reviewed after upstream releases.
Related WPStack guides
Frequently asked questions
Why does remove_action('admin_notices', ...) not work?
The banner may be inserted by JavaScript after PHP notice hooks finish, or it may use a different admin surface.
Can I dequeue the plugin’s admin script?
Only if the exact handle is promotional-only. Shared bundles may also provide settings, security or license functions.
Is MutationObserver expensive?
It can be if it watches the whole DOM and rescans repeatedly. Scope the root, inspect added nodes and disconnect when possible.
Should I match the banner text?
Not alone. Wording and translations change, and generic terms create false positives. Combine stable plugin-owned attributes and component structure.
Does removing the DOM node stop tracking requests?
No. The script may already have fetched or reported data. Inspect network behavior separately.
References
- WordPress script enqueuing
- WordPress admin_enqueue_scripts hook
- MDN MutationObserver
- WordPress admin_notices hook

Aditya Bhimrajka is a technology entrepreneur, product strategist, and software solutions expert with over a decade of experience building scalable web and mobile applications. His expertise spans SaaS, AI, cloud technologies, custom software development, and digital transformation. Passionate about solving real-world business challenges through technology, Aditya shares practical insights on WordPress, plugins, software development, startup growth, product strategy, and emerging technologies. At WPStack, he writes actionable, experience-driven content that helps developers, businesses, and website owners build secure, high-performing, and future-ready WordPress solutions.