
Which WordPress Autoloaded Options Are Safe to Disable?
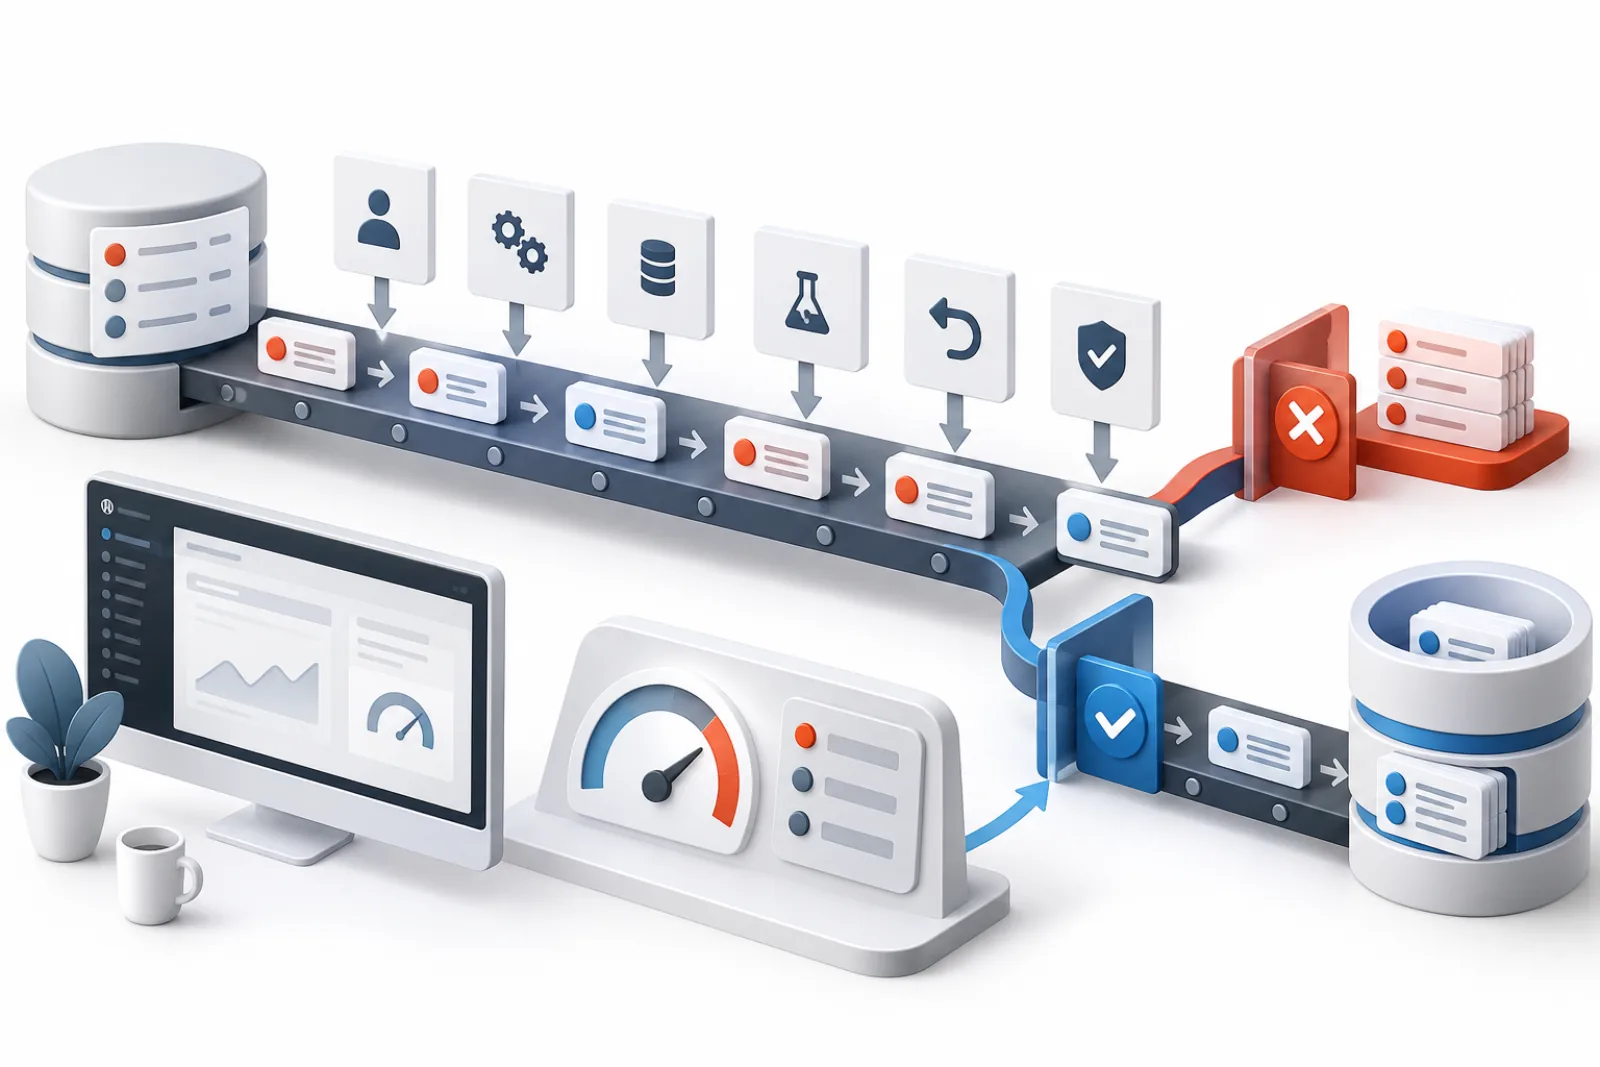
No universal list can tell you which WordPress autoloaded options are safe to disable. An option is a candidate only when evidence shows it is not required on most requests, its owner is known, a backup exists, and the change survives real page and admin tests. Names such as theme_mods_*, rewrite_rules or plugin prefixes are clues—not permission.
This guide provides a decision process that reduces always-loaded data without deleting configuration or breaking a plugin.
Disable autoloading before considering deletion
Changing an option from autoloaded to on-demand leaves its value available through get_option(). Deleting the row removes the value. For a valid but infrequently used setting, disabling autoload is usually the safer first experiment. Deletion belongs to records confirmed obsolete through ownership, code and runtime evidence.
| Evidence | Interpretation | Next step |
|---|---|---|
| Read on nearly every public request | Autoload may avoid repeated lookups | Keep and investigate size at the source |
| Read only on one settings screen | Strong on-demand candidate | Test autoload off on staging |
| Owner plugin is deactivated | Probably unused now, possibly needed on reactivation | Disable autoload; preserve until uninstall decision |
| No owner and no observed reads | Possible abandoned record | Snapshot, widen observation, then quarantine |
| Large serialized value that changes often | Design problem and cache churn risk | Contact owner; avoid manual editing |
Step 1: measure bytes, not just rows
Start with total autoloaded bytes and the largest individual values. WordPress 6.6 introduced a Site Health critical threshold of 800,000 bytes and dynamically avoids autoloading some newly written values larger than 150,000 bytes when the caller does not explicitly require autoloading. Those defaults are investigation signals, not guarantees that a particular site will be slow.
Record WordPress version, object-cache status, total bytes, largest rows, request latency and PHP memory before changing anything.
Step 2: identify the real owner
Search active and inactive plugin code, the current and previous theme, must-use plugins and deployment history for the option name. Prefixes help, but shared libraries and renamed products can mislead. Check when the row was last changed if an activity log or database audit exists. Ask the vendor when a commercial plugin owns a large or opaque value.
Step 3: observe runtime use
Exercise representative routes on staging: homepage, posts, search, account, checkout, cron, REST, AJAX, login and the owner’s settings screen. Record whether the application requests the option and whether it happens before or after the all-options cache is primed. A short observation on the homepage cannot prove an option is unused by scheduled tasks or rare workflows.
Step 4: classify risk
- Keep autoloaded: small, stable and required across most requests.
- Disable autoload: valid but confined to rare admin or feature routes.
- Quarantine: owner uncertain; disable autoload and observe before deletion.
- Delete only after proof: abandoned, backed up and absent from all required workflows.
- Escalate: core-like, security, routing, role, cron or serialized data whose schema is unclear.
Step 5: change one controlled batch
- Back up the database and export each candidate’s exact name, value and autoload state.
- Use a staging copy representative of production.
- Change autoload state through supported WordPress functions or a tool that preserves the value.
- Clear the relevant object-cache entry so the test does not read stale state.
- Run the route matrix and background jobs.
- Compare performance and errors with the baseline.
- Deploy a small batch during a monitored window and retain rollback data.
Worked example
A 420 KB option belongs to an active analytics plugin and is read only on its report screen. Staging shows no public, checkout, cron or REST reads. Disabling autoload reduces the all-options payload; the report screen performs one on-demand lookup and still works. This is a defensible change. If the same value were read on every request, the correct fix would be to reduce or restructure it with the plugin owner—not merely move the cost into repeated database calls.
Route coverage checklist
Build the test matrix from the site’s real revenue and editorial paths. A brochure site may need homepage, search, contact form, login and scheduled publishing. A WooCommerce store should add product variations, cart fragments, checkout, payment callbacks, subscriptions, order email and refund flows. Membership and LMS sites need enrollment, access checks, progress, renewals and expiry. Multilingual sites must test each active language because translated settings may use different options.
Run scheduled hooks and CLI maintenance separately. An option absent from browser traffic may still configure backups, imports or feeds. Record every route tested so “unused” means “not observed across this defined coverage,” not an impossible universal claim.
Rollback triggers
Restore the original state when error logs change, a critical path fails, on-demand queries multiply unexpectedly, cache latency rises or business data differs. The rollback record must contain the exact previous autoload value—not simply “turn it back on”—because modern WordPress distinguishes explicit and automatic states.
Inspect the active autoload set safely
Run discovery through WordPress where possible so the application uses the same autoload-value policy as the installed core version. Export option name, serialized byte size, stored state and a hash of the value. Keep the actual value in an access-controlled backup; reports rarely need to expose tokens, email settings or other sensitive configuration.
Rank by bytes first, then examine the distribution. One 900 KB report and nine hundred small settings require different remedies. Add a cumulative total so reviewers can see which few candidates account for most of the payload. Record whether a persistent object cache is active, but do not treat it as permission to ignore large values.
| Inventory field | Purpose | Safety note |
|---|---|---|
| Option name | Ownership and code search | Can still reveal plugin or tenant details |
| Serialized bytes | Request-wide payload contribution | Measure stored bytes, then verify PHP memory separately |
| Stored autoload state | Explicit versus automatic intent | Interpret with the current WordPress value list |
| Value hash | Detect change during review | Do not publish the underlying secret-bearing value |
| Owner and confidence | Routes questions and approval | Prefix matching alone is low-confidence evidence |
Build an ownership dossier
Search option names and stable fragments in active, inactive and must-use plugins, the current and previous themes, deployment scripts and internal integrations. Check plugin documentation, uninstall behavior and changelogs. For dynamically constructed names, search the prefix and the wrapper that calls get_option() or update_option().
Record whether the owner is active, whether the feature is enabled, where the value is written and what happens if it is missing. A default that can be regenerated differs from an authentication token or a complex configuration. Ask the product owner or vendor when code evidence is incomplete.
Do not publish option values in support tickets. Provide the name, byte size, state, version, relevant call path and sanitized structure. A serialized value may contain credentials or customer data even when its option name looks harmless.
Observe reads without treating absence as proof
Instrument a staging copy using an option-specific hook, application profiler or narrowly scoped logging. Record route, request type, time and call stack without writing the value. Cover public pages, admin screens, authenticated accounts, checkout, webhooks, REST, AJAX, cron and command-line maintenance.
Observation has a boundary. A one-day test cannot rule out monthly renewals, seasonal imports or disaster-recovery paths. Write the coverage and duration beside every decision. Combine runtime evidence with code, ownership and business schedules.
Beware of the all-options cache: code can obtain an autoloaded value without a separate database query, while a profiler may show only the grouped load. Trace calls to the Options API or the owning abstraction, not query logs alone.
Score candidates by value, cost and uncertainty
Use a decision table rather than an automatic threshold. Favor autoload-off when the value is large, read rarely, stable, recoverable and owned. Increase caution when it controls authentication, routing, roles, scheduled work, object-cache keys, rewrite behavior or a business-critical integration.
| Factor | Lower-risk signal | Higher-risk signal |
|---|---|---|
| Runtime frequency | One known settings or report screen | Public, login, checkout or background routes |
| Recoverability | Exact snapshot and tested restore | Unknown schema or external state |
| Ownership | Active owner and documented behavior | Shared prefix or dynamic name |
| Change rate | Stable configuration | Rewritten frequently or used as a log |
| Failure consequence | Optional admin report unavailable | Authentication, revenue or data integrity affected |
Use the score to prioritize human review, not to execute changes. Two sites can assign different risk to the same plugin option because their enabled features and business paths differ.
Change the state through supported APIs
Use wp_set_option_autoload() or the appropriate batch function available in the installed WordPress version. These routes update cache state consistently and express intent better than raw SQL. Confirm the return value and re-read the option’s stored state after cache invalidation.
Do not alter the serialized value while changing autoload behavior. The experiment should isolate one variable. If the owning plugin rewrites the row and restores its old state, fix the write path or work with the vendor instead of repeatedly forcing the database column.
Measure whether the change helped
Compare all-options bytes, PHP peak memory, database and object-cache calls, server response time and error rate on the same route matrix. Use cold and warm cache states with realistic concurrency. An autoload reduction can decrease request memory yet add an on-demand lookup to one route; report both effects.
Do not promise a fixed speed gain from removed bytes. PHP version, serialization, cache topology, worker count and code paths all matter. Retain a change only when it reduces a measured cost or materially lowers operational risk without regressions.
Worked example: a disabled plugin retained for reactivation
A marketing plugin is temporarily inactive but retains a 520 KB audience cache and 18 KB of configuration. Code and vendor documentation show the cache can rebuild; the configuration is needed for reactivation. The site disables autoload for both during the inactive period but does not delete either.
After reactivation on staging, the plugin reads its settings on its own routes and rebuilds the cache. If the plugin explicitly restores required autoload behavior, that becomes part of the lifecycle test. The result protects current requests without destroying the planned return path.
Worked example: a core-like option that should remain
An audit ranks rewrite_rules highly by size. It appears tempting because administrators rarely edit permalinks. However, WordPress uses rewrite rules to route ordinary requests, so “rare settings screen” reasoning is wrong. The site keeps it autoloaded and investigates why the rule set is unusually large—often excessive registered routes or content structures.
This is why name lists are dangerous. The same measurement that finds a large option must be followed by execution-path understanding.
Handle Multisite and network options
Audit each site’s options table and network metadata separately. A subsite option may be unused locally while a network-active plugin expects a network-level setting. Test super admin, site admin, site creation, domain mapping and network cron. Record blog ID with every snapshot and change.
Roll out in rings: staging network, one low-risk subsite, representative business sites, then the fleet. A query that loops across hundreds of sites can itself cause load, so inventory in bounded batches and schedule it away from peak traffic.
Create a durable change record
Store option name, site ID, owner, plugin and WordPress versions, bytes, original value hash and protected export, original state, new state, evidence, approver, deployment time, tests and observation result. Include the exact API route used for rollback.
Recheck after plugin activation, upgrade, migration or WordPress policy changes. Remove stale exceptions when the option disappears or its owner fixes the storage model. Autoload maintenance succeeds when each change remains explainable, not when a dashboard briefly shows a smaller number.
Recognize option categories that need extra caution
Core routing, role and capability, active theme, cron, authentication, multisite, rewrite and object-cache coordination values can affect broad request behavior. Security plugins may store rules or keys that appear opaque. Commerce and membership plugins may perform access decisions before their main page renders. Do not change these because a generic list labels them “large.”
Transients have separate lifecycle semantics and can be stored in options when no persistent object cache is present. Expired transient cleanup differs from changing a durable configuration’s autoload flag. Likewise, a plugin cache that is rebuildable may still need its owner to invalidate and regenerate it safely.
Serialized arrays require whole-value integrity. Never delete a member or alter string lengths with ad hoc SQL. If one component is large, ask the owner to split the data through a schema-aware release.
Investigate unexpected on-demand query growth
After moving a value off autoload, the first get_option() normally performs an individual lookup and then uses the request cache. Repeated queries for the same option can indicate cache invalidation, switching sites, custom wrappers or code that bypasses the Options API. Capture the call pattern before reverting or scaling the change.
With a persistent object cache, the on-demand value may be served from its own cache key. Measure hit latency and payload size. A remote cache can make many small lookups expensive even when its hit ratio is high. Compare end-to-end route time rather than counting queries in isolation.
Use an observation window that matches the business
Monitor PHP errors, database and cache latency, memory, failed jobs, payment and form outcomes, login issues and support reports. Include at least one execution of weekly or monthly workflows touched by the owner. For seasonal features, either test the path deliberately or keep the candidate quarantined until the relevant period.
Define rollback thresholds before deployment. One fatal error, failed authentication path or incorrect transaction can justify immediate reversal; small timing variance should trigger more measurement. Name the operator authorized to restore the previous state.
Worked case: frequent writes make the grouped cache expensive
A plugin stores a 300 KB integration status map in an autoloaded option and rewrites it every minute. Public requests read only a 2 KB configuration subset. The problem is not just initial bytes: every write invalidates the shared all-options cache and forces workers to receive a new serialized collection.
Disabling autoload reduces the blast radius, but the durable fix belongs in the plugin. The owner separates stable configuration from volatile status and stores operational history in a suitable table. Tests cover public requests, the integration dashboard, scheduled refresh and cache loss.
Worked case: a feature flag used before most routes
A 200-byte option appears unimportant by size but controls whether a membership gate runs on every request. Moving it off autoload saves almost nothing and adds an individual lookup. The audit keeps it on. Optimization effort shifts to the few large, admin-only values that dominate the payload.
This illustrates why the decision combines bytes and frequency. The safest list is not “large off, small on”; it is a documented set of owner intentions verified against real execution.
Prepare for vendor support
Send a sanitized package containing plugin and WordPress versions, option name, serialized size, stored state, update frequency, routes observed, stack trace or owning call, object-cache status and the measured impact. Ask whether the value is required on most requests, can be split, or is safe on demand.
Do not ask a vendor to approve deletion without explaining retention and enabled features. Preserve their response in the change record and revalidate after major upgrades.
Definition of done
- The current autoload set and total bytes are measured with version-aware logic.
- Every changed option has a confirmed owner, runtime coverage and protected snapshot.
- Only the autoload state changed during the experiment.
- Public, admin, background, authentication and business routes pass.
- Performance and cache behavior are measured under representative conditions.
- The observation period completes without attributable errors.
- Rollback remains tested and the decision record has an owner and review date.
Post-deployment verification worksheet
Immediately after release, confirm the stored state, total autoload bytes and value hash for every changed option. Run one uncached and several warm requests across the route matrix. Trigger scheduled work explicitly where safe. Compare PHP errors, query counts, object-cache calls, peak memory and response time to the baseline.
At the end of the observation period, confirm no owner has rewritten the state, no support report maps to the change, and rare workflows completed. Record benefits and costs separately. If public requests improved but an essential report became materially slower, involve the owner rather than declaring unconditional success.
Prevent the payload from growing back
Schedule a version-aware inventory and alert on material byte growth, new unusually large rows and frequent writes to large autoloaded values. Route findings to owners with the option name, size delta and first-seen release. Do not automatically flip new rows in production.
For internally developed plugins, add storage reviews to feature design. State the maximum expected value size, read frequency, write frequency and lifecycle. Tests should assert explicit autoload intent for important options. Prevention costs less than rediscovering the same owner after the Site Health warning returns.
Keep the inventory read-only by default and require an explicit reviewed batch for changes. Separate the account that can inspect option names and sizes from the account authorized to modify production. This reduces the chance that an exploratory audit becomes an accidental cleanup.
When a candidate remains uncertain, leave it on demand and revisit after a longer observation window. Preserving a recoverable value costs less than reconstructing undocumented configuration. The goal is controlled request loading, not deletion for its own sake.
Retain final accountable approval with the exact production verification evidence.
Record the final reviewer.
How Autoloaded Options Manager helps
Autoloaded Options Manager surfaces option size, ownership clues, risk signals and current autoload state, and it supports snapshot and rollback around controlled changes. It accelerates evidence gathering; it cannot know every custom code path or business requirement.
Related WPStack guides
Frequently asked questions
Is it safe to disable every large option?
No. A large value may be needed on most requests. Measure use and owner behavior first.
Will get_option() still work?
Yes, when only autoloading is disabled. WordPress fetches the preserved option on demand.
Are inactive-plugin options safe to delete?
Not automatically. They may be needed if the plugin is reactivated. Disable autoload first and delete only as part of a deliberate uninstall decision.
Should I edit serialized values?
Avoid manual editing unless you understand the serialization and schema. Changing string lengths incorrectly can corrupt the value.
References
- WordPress 6.6 Options API autoload changes
- WordPress 6.4 option autoload functions
- WordPress: wp_set_option_autoload()

Aditya Bhimrajka is a technology entrepreneur, product strategist, and software solutions expert with over a decade of experience building scalable web and mobile applications. His expertise spans SaaS, AI, cloud technologies, custom software development, and digital transformation. Passionate about solving real-world business challenges through technology, Aditya shares practical insights on WordPress, plugins, software development, startup growth, product strategy, and emerging technologies. At WPStack, he writes actionable, experience-driven content that helps developers, businesses, and website owners build secure, high-performing, and future-ready WordPress solutions.