How to Clean Up Autoloaded Options Left Behind by Deleted WordPress Plugins
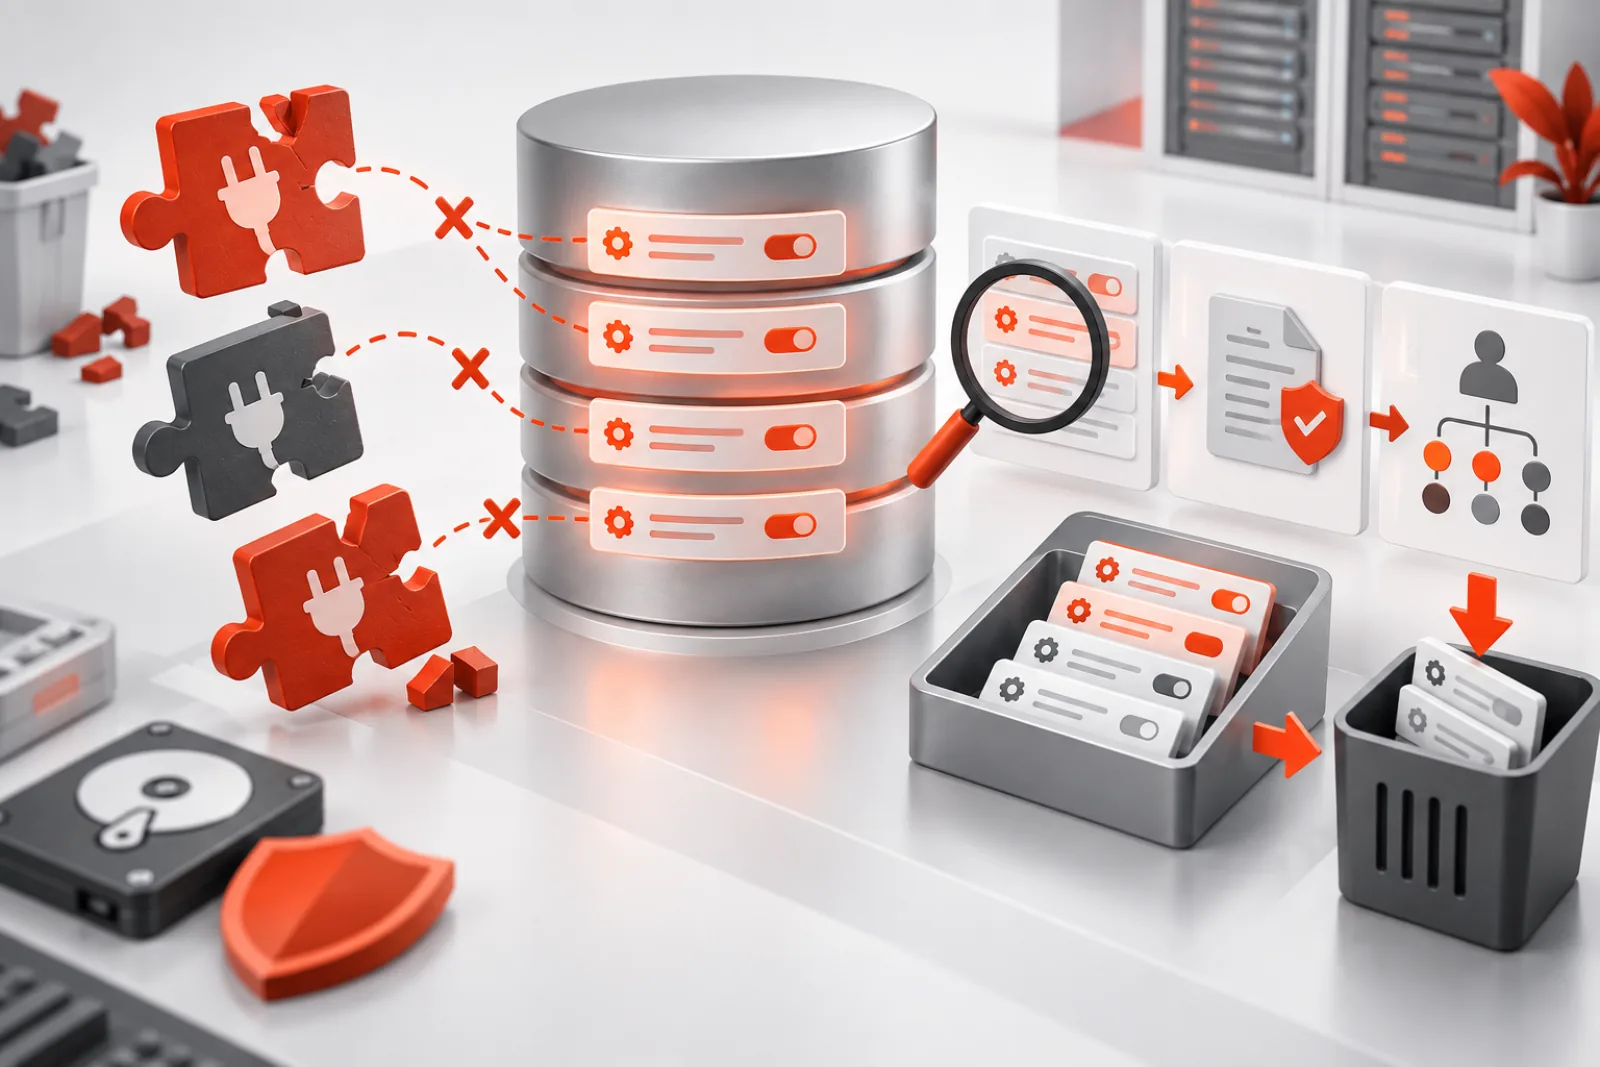
Options left by deleted WordPress plugins are candidates for investigation, not automatic deletion. Some are abandoned settings; others belong to shared libraries, migration history, a premium companion, a must-use plugin or a product that may be reinstalled. Deleting by prefix can break another component or destroy configuration the owner expected to preserve.
This cleanup runbook prioritizes reversible autoload reduction, ownership evidence and a defined observation period.
Why plugins leave data behind
WordPress distinguishes deactivation from uninstall. Deactivation should normally preserve settings so reactivation works. Uninstall may remove data, but plugins often offer a “retain data” choice, lack a complete uninstaller, or intentionally preserve records for upgrades and shared extensions.
| Clue | What it suggests | Risk |
|---|---|---|
| Unique old plugin prefix | Possible abandoned settings | Prefix may be reused by a suite |
| Recent writes | Something still owns the row | Do not delete |
| Read during cron or REST | Background or integration dependency | High |
| Large autoloaded serialized record | Performance candidate | Schema may be fragile |
| No code reference anywhere | Stronger abandonment evidence | Runtime-generated names can evade search |
Build the candidate inventory
- Back up the database and record its restore point.
- Export option name, exact value, byte size and autoload state.
- Search active, inactive and must-use plugins plus current and old themes.
- Review deployment history and uninstall documentation.
- Observe reads and writes across public, admin, cron, REST, AJAX and CLI workflows.
- Assign an owner, confidence and reason to each candidate.
Use a quarantine stage
For an apparently abandoned option that is still autoloaded, disable autoload first while preserving the value. Clear the relevant object-cache entry, exercise the route matrix and observe production through a normal business cycle. This immediately removes it from the always-loaded payload while retaining a simple rollback.
Choose the observation period based on the site. Monthly billing, annual renewals and seasonal integrations require longer coverage than a brochure site.
Know what code search cannot prove
Plugins can construct option names dynamically, read them through wrappers, or use a shared SDK. Database prefixes can outlive product rebrands. A multisite installation may store network settings in sitemeta rather than a site’s options table. Search is useful negative evidence only when combined with runtime and ownership checks.
Deletion approval checklist
- The owning product is permanently removed or the vendor confirms the record is obsolete.
- No active code, background job or network component reads or writes it.
- The exact value and state are exported.
- Autoload-off quarantine completed without regression.
- A reviewer approved the batch and reason.
- Rollback has been tested on staging.
- Post-delete monitoring covers the relevant business cycle.
Worked investigation
An audit finds 70 options with an old plugin prefix, including a 600 KB autoloaded cache. Code search finds no active product, but a must-use integration references two authentication options and a monthly cron callback reads a third. The correct batch excludes those three, disables autoload for the remaining candidates and observes a full monthly cycle. Only then are confirmed cache and UI-preference rows approved for deletion.
A prefix-only cleanup would have broken the integration. Runtime and background coverage turned a plausible assumption into a defensible decision.
Separate configuration, cache and records
Classify values by purpose. Rebuildable caches and expired transients generally have lower retention value. Configuration may be needed on reinstall. Tokens require secure revocation, not merely deletion. Consent or audit records may have legal retention requirements. Large arrays can mix categories, which is a reason to involve the original owner rather than editing individual serialized members.
Maintain an evidence ledger
For each batch, save candidate names, sizes, original states, ownership sources, routes observed, approval, quarantine dates, deletion result and rollback location. The ledger prevents repeat investigation and provides a trail when a later plugin install expects historical settings.
Delete through a controlled batch
Use supported WordPress APIs or a maintenance tool that handles cache invalidation. Keep batches small and never modify the inside of a serialized option as a shortcut. After deletion, run page, login, checkout, scheduled task, integration and admin tests; inspect logs; and compare the autoload inventory and request baseline.
Developer responsibility
Plugin authors should document retention, implement uninstall behavior deliberately, and use the WordPress 6.4 autoload functions during deactivation when preserved settings are no longer needed on every request. Destructive uninstall must require an explicit product decision, especially for shared or regulated data.
Start with a read-only ownership report
Export option name, serialized bytes, autoload state, value hash and site ID. Add active, inactive, must-use and theme code matches, last observed read or write, installation history and vendor documentation. Keep raw values in a protected backup rather than the working report because options can contain credentials and personal data.
| Ownership evidence | Confidence | Limitation |
|---|---|---|
| Exact name in active code and runtime stack | High | Other components may share the value |
| Vendor uninstall documentation | High when version matches | Local extensions may depend on retained data |
| Distinctive prefix in removed plugin | Medium | SDKs and product suites reuse prefixes |
| No repository match | Low negative evidence | Names can be dynamic or remote code absent |
| Old update timestamp | Low | Stable valid settings may never change |
Assign “unknown” openly. A cleanup report is more trustworthy when it distinguishes uncertainty instead of converting every unmatched prefix into abandoned data.
Understand deactivation, uninstall and deletion
Deactivation stops a plugin’s normal hooks but should often preserve settings for reactivation. Uninstall is the product’s chance to remove data according to its documented policy, sometimes after an explicit “delete data” choice. Deleting plugin files outside WordPress may bypass that uninstall route entirely.
Review whether a premium and free edition share settings, whether add-ons remain active, and whether a must-use bridge expects the data. A renamed plugin may adopt the same rows. Test reinstall and reactivation on staging before deciding retained configuration is useless.
Classify retained values by purpose
Separate durable configuration, user preferences, caches, transients, logs, job state, authentication secrets, consent records and migration markers. Each category has different retention and recovery rules. A rebuildable report cache is not equivalent to a payment token or proof of consent.
Large serialized options may combine several categories. Do not remove selected members without the schema and owner. If the product is still maintained, ask it to provide a migration or cleanup routine that preserves integrity.
Quarantine before permanent deletion
For candidates currently autoloaded, move them off the request-wide path through supported WordPress APIs while preserving values. Record the exact original state and clear relevant object caches. Exercise public, admin, login, REST, AJAX, cron, CLI, webhook and business workflows.
Keep the quarantine through a business-relevant observation window. Monthly renewals, tax exports, backups and seasonal feeds require deliberate testing or longer time. If anything reads or rewrites the option, stop and reassign ownership.
Quarantine provides immediate payload reduction without pretending deletion is proven. It also makes rollback a state change rather than data reconstruction.
Back up for item-level restoration
Capture exact option names, values, serialized form, autoload states, database prefix, site IDs, timestamps and hashes. Encrypt the archive, restrict access and store it outside the production database. Test restoration of one representative value on staging, including cache invalidation.
A full database backup is necessary but can be a poor first rollback on an active store because it overwrites newer orders and content. The batch export allows precise recovery. Keep the full backup for unknown structural damage.
Handle secrets and external integrations
Deleting an API key from WordPress does not revoke it at the provider. Identify credentials, webhooks and tokens in the candidate set; revoke or rotate them through the owning service when the integration is retired. Preserve only the minimum audit evidence and do not place raw values in tickets.
Check queued actions and scheduled events that may still attempt the integration after its plugin is gone. Remove them only through a schema-aware workflow after confirming ownership. An orphaned job can recreate options or generate repeated errors.
Respect legal and contractual retention
Some options can contain consent history, tax configuration, transaction references or records required by policy. Technical inactivity does not override retention obligations. Ask the responsible business or legal owner, document the basis and apply secure deletion only when approved.
Conversely, privacy obligations may require timely removal of personal data. Classify the content, not just the plugin name. A product’s “retain settings” default may be inappropriate after account closure if the setting embeds personal information.
Use small deletion batches
- Freeze the reviewed candidate list and confirm hashes have not changed.
- Verify backup retrieval, approval and rollback responsibility.
- Delete through
delete_option()or the product’s supported uninstaller. - Clear relevant caches and confirm each row’s final state.
- Run the defined route and background test matrix.
- Monitor errors, integrations and business outcomes through the observation window.
- Record deleted, skipped, restored and unexpectedly rewritten results separately.
Never execute a wildcard prefix deletion on production. Review each item or a versioned schema-approved set. Stop the batch when an option changes after approval or a regression appears.
Worked case: free and premium editions share settings
An agency deletes the free plugin and finds twelve options with its prefix. The premium companion remains active and uses five of them through a shared SDK. Runtime traces show three more configure a must-use integration. Only four cache and onboarding values are truly abandoned.
The team excludes the eight active dependencies, disables autoload for the four candidates and observes. After vendor confirmation and a reinstall test, it deletes the four through a controlled batch. Prefix-only automation would have broken production.
Worked case: a monthly job defeats a short observation
A reporting plugin was removed, and its options show no reads during a one-week test. On the first day of the next month, a custom cron integration reads one retained mapping to generate finance exports. The option is no longer owned by the deleted plugin alone.
Restoration from the batch export recovers the job. The team moves the mapping into the integration’s own configuration, adds a monthly-route fixture and restarts quarantine. The incident demonstrates why observation scope must reflect business schedules.
Audit Multisite carefully
Each subsite has its own options table, while network settings live separately. A plugin can be network-active, site-active on selected blogs or replaced by a must-use component. Include blog ID, activation scope and network ownership in every candidate.
Inventory in bounded batches so switching through hundreds of sites does not overload the database. Test site creation, Network Admin, domain mapping and shared scheduled jobs. Roll out deletions to a low-risk ring before the full network.
Monitor for recreation and regressions
After deletion, watch PHP errors, failed cron, integration health, cache misses, login, checkout and support reports. Re-scan candidate names. A recreated row means active code still owns it; investigate the write path instead of deleting it repeatedly.
Compare all-options bytes and request behavior to the baseline, but do not make performance the only acceptance criterion. Configuration correctness, retention compliance and recovery evidence matter equally.
Prevent abandoned options in plugin development
Document every durable option, owner, schema, autoload intent, activation behavior, deactivation behavior, uninstall policy and maximum size. Provide an explicit delete-data choice where appropriate and test uninstall with shared add-ons. Use public WordPress APIs so caches remain coherent.
Separate volatile caches and logs from configuration. During upgrades, remove superseded rows through versioned migrations with backups and tests. Good lifecycle design prevents administrators from guessing years later.
Definition of done
- Every deleted option has documented ownership and retention approval.
- Exact protected values and states can be restored individually.
- Autoload-off quarantine passed the complete route and business-cycle test.
- Shared libraries, add-ons, must-use plugins and network scope were checked.
- Secrets were revoked or rotated at their provider.
- Deletion used supported APIs in a small reviewed batch.
- No errors, recreation or business regressions appear during observation.
Know the limits of repository search
Code may construct an option name from a site ID, account ID or feature slug. It may call a wrapper whose final key appears only at runtime, load a shared library from vendor, or receive configuration from a must-use plugin outside the normal project repository. Search exact names, prefixes and Options API wrappers.
Include deployment artifacts matching production, not only source branches. Optimized builds, premium modules and host-provided code can differ from the developer checkout. A lack of text match remains evidence of uncertainty, not permission to delete.
Review custom tables and user metadata alongside options
Removing options may leave a plugin’s custom tables, user metadata, post metadata, scheduled actions, roles, uploads and object-storage files behind. Conversely, another active component may use those records together with the option. Map the product’s whole data model before running a partial cleanup.
Do not broaden an options task into automatic table deletion. Inventory each storage class, owner and retention separately. Custom tables often need foreign-key or application-aware order, and deleting them can be far more destructive than removing a cache option.
Separate expired transients from abandoned configuration
Transients are cached values with expiration semantics, although external object caching can change where they are stored. Use supported transient cleanup behavior and verify the owning feature can rebuild data. Do not treat every option with a transient-like name as safely expired without interpreting its timeout pair and cache backend.
A large durable option that resembles a cache but has no expiration still needs ownership review. Ask whether the plugin intentionally persists it, how it invalidates the value and what happens during a cache miss.
Prepare a vendor escalation package
Provide product and WordPress versions, option names, sizes, states, sanitized structure, installation and activation history, code and runtime evidence, observation window and intended retention. Ask which values are shared, rebuildable, required for reactivation or safe to remove through an official tool.
Keep vendor responses with the batch. Advice for one release may become stale after schema changes, so recheck version applicability. Never send raw credentials or customer-derived values.
Create a machine-readable batch manifest
For each candidate, store site ID, option name, value hash, bytes, state, category, owner, evidence references, quarantine start and result, deletion approval and final disposition. At batch level, store database recovery point, tool version, operator, reviewer, start and finish time and observation deadline.
Append actual outcomes rather than overwriting proposals. “Skipped because the value changed” and “restored after monthly job failure” are important controls. A manifest makes later audit and item-level rollback possible without searching terminal history.
Stop when evidence changes
Recompute hashes immediately before changing state or deleting. If a value changed after review, remove it from the batch and identify the writer. If the former plugin is reinstalled, an add-on activates or a business owner revives the integration, restart ownership assessment.
Do not force the original plan through a changed environment. The safest batch is allowed to become smaller. Record the skip reason and schedule a new review when the system stabilizes.
Worked incident: direct SQL leaves stale cached data
An operator deletes rows with SQL and confirms they are absent from the table, but some workers continue reading values from the persistent object cache. Behavior differs across requests, and a plugin later writes part of the configuration back.
The team restores the batch, clears caches through the supported integration and repeats deletion with delete_option(). It adds cache-coherence verification and removes raw SQL from the normal runbook. Database state alone had not described application state.
Measure the cleanup outcome honestly
Report options investigated, moved off autoload, deleted, skipped, restored and recreated. Add bytes removed from the all-options set, database bytes reclaimed only after storage maintenance, performance measurements, errors and restore tests. Avoid presenting row count as user benefit.
Review at one week and after the longest relevant business cycle. A clean Site Health screen is useful, but stable logins, payments, scheduled work, integrations and recoverability are the real acceptance evidence.
Retire the backup securely
Keep item-level exports through the observation and contractual retention period, then delete them from primary and copied locations through an approved lifecycle. Document destruction. Backups may contain the same secrets or personal data that motivated cleanup.
Before expiry, confirm the final manifest, reviewer sign-off and absence of unresolved incidents. If one candidate remains disputed, retain only the required subset rather than extending every batch file indefinitely.
Create a recurring hygiene review
After plugin removal, schedule a review that compares installed products, active option owners, autoload bytes, scheduled actions and custom tables. Route new unmatched values for investigation; do not delete them automatically. Annotate installations, upgrades and migrations so ownership changes have context.
For managed fleets, sample sites by business class and plugin mix. One brochure site’s clean result does not prove a store or membership site is safe. Track recurring offenders and ask vendors to improve uninstall and data-retention behavior.
Close each review with assigned actions, not a growing spreadsheet. Options that remain intentionally retained should have an owner, purpose and next review date so they stop appearing as unexplained candidates.
Retain one restored test option as evidence that the current archive and procedure still work. Repeat the drill after database, cache or hosting changes; recovery assumptions age as quickly as cleanup rules.
Record the recovery drill date, operator, result and next required review.
How Autoloaded Options Manager helps
Autoloaded Options Manager organizes candidate options by size, state and likely owner and supports safer snapshots and reversible changes. It cannot determine contractual retention or every dynamically generated dependency, so deletion remains a reviewed operation.
Handle uncertain ownership conservatively
Prefixes are clues, not proof. A vendor may rename a plugin, share an SDK or retain data for reactivation. Search source and vendor uninstall documentation, then quarantine uncertain candidates. For serialized values, do not edit fragments in SQL. Preserve the exact original and test both normal site behavior and the former plugin’s reinstall path.
Related WPStack guides
Frequently asked questions
Can I delete every option with an old plugin prefix?
No. Verify shared libraries, companion plugins, dynamic use and retention intent.
Why not delete on deactivation?
Users commonly deactivate temporarily. WordPress provides a separate uninstall lifecycle for deliberate data removal.
Does disabling autoload remove the setting?
No. It preserves the value and makes WordPress fetch it on demand.
What about Multisite?
Audit each site and network-level metadata separately; ownership and retention may differ across the network.
References
Aditya Bhimrajka is a technology entrepreneur, product strategist, and software solutions expert with over a decade of experience building scalable web and mobile applications. His expertise spans SaaS, AI, cloud technologies, custom software development, and digital transformation. Passionate about solving real-world business challenges through technology, Aditya shares practical insights on WordPress, plugins, software development, startup growth, product strategy, and emerging technologies. At WPStack, he writes actionable, experience-driven content that helps developers, businesses, and website owners build secure, high-performing, and future-ready WordPress solutions.