Building Custom Rate Limiting Middleware for the WordPress REST API
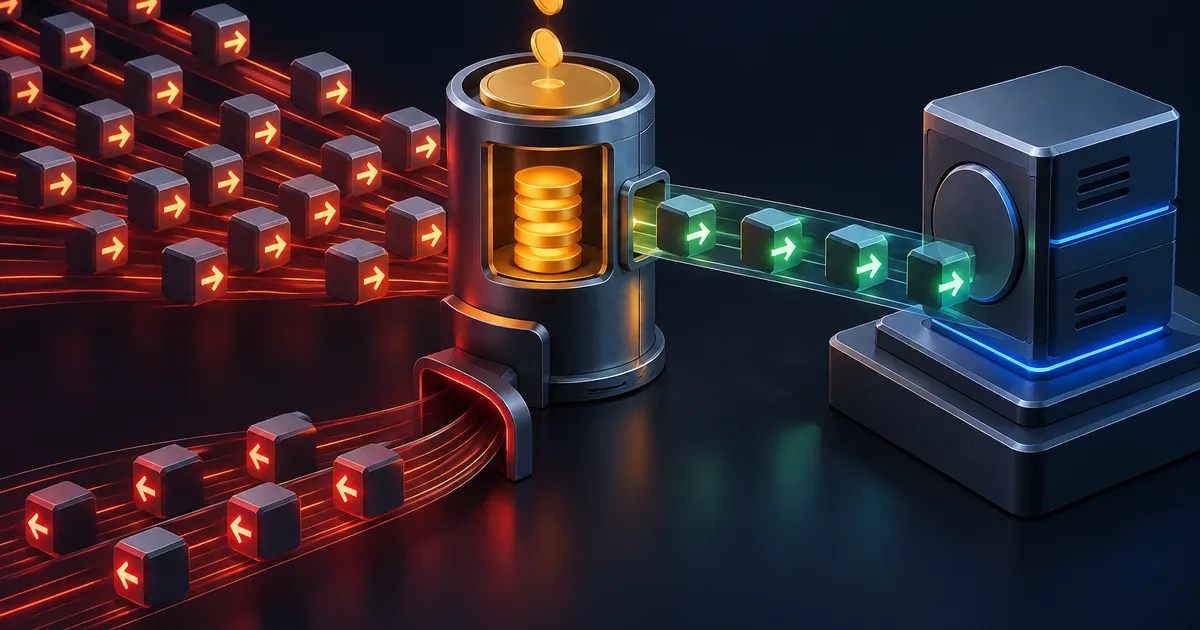
Protect custom REST endpoints from scraping and DDoS attacks. Redis sliding-window log rate limiter implementation with standard Retry-After HTTP headers.
The WordPress REST API is the architectural backbone of modern headless applications, mobile app backends, decoupled frontend architectures, and high-frequency third-party integrations. By exposing structured JSON endpoints across /wp-json/wp/v2/ and custom vendor namespaces, WordPress enables seamless data exchange across diverse client platforms.
However, out of the box, WordPress provides zero built-in rate limiting capabilities for its REST API. Without proactive rate limiting, a single rogue script or coordinated botnet can flood custom database endpoints, exhaust PHP-FPM worker pools, hammer MySQL with unindexed queries, and trigger complete application outages. Furthermore, sensitive endpoints—such as user registration, checkout submission, coupon verification, and AI inference proxies—become lucrative targets for brute-force attacks and credit card testing fraud.
Threat Modeling: Common REST API Abuse Vectors
Modern WordPress applications face diverse automated threats targeting exposed REST endpoints:
- Distributed Credential Stuffing: Botnets iterate through millions of leaked email/password combinations against
/wp-json/jwt-auth/v1/tokenor custom authentication endpoints, causing severe CPU spikes due to repetitive password hashing. - Content & Price Scraping: Competitors scrape catalog data, dynamic inventory counts, and proprietary post content via
/wp-json/wp/v2/postsor WooCommerce product endpoints, degrading database performance and stealing intellectual property. - Carding & Checkout Fraud: Fraud rings submit thousands of micro-transactions via payment gateway REST controllers to validate stolen credit card numbers, resulting in massive merchant chargeback fees and payment processor bans.
- Resource Exhaustion (Denial of Wallet): Complex search endpoints executing full-text SQL queries or heavy AI inference proxies (e.g. OpenAI embeddings) are repeatedly queried to exhaust server RAM and cloud API quotas.
- Inventory Sniping: Automated scalper bots continuously poll flash sale checkout endpoints to lock up cart items before authentic human consumers can complete purchases.
Evaluating Rate Limiting Algorithms
Selecting the appropriate rate limiting algorithm depends on the trade-off between memory consumption, burst handling, and computational overhead. Let us compare the four primary algorithms:
Frequently Asked Questions
WordPress Core is designed to run in minimal shared hosting environments without mandatory external dependencies like Redis. Because effective high-concurrency rate limiting requires an in-memory key-value store, it is left to custom plugins and infrastructure proxies.
Always return HTTP status code `429 Too Many Requests` along with a `Retry-After` header indicating the number of seconds the client must wait before making another request.
Check for `defined(‘DOING_CRON’) && DOING_CRON` or verify internal HMAC server authorization tokens in your middleware to bypass rate limits for trusted internal tasks.
Cloudflare provides Edge Rate Limiting to block massive Layer 7 DDoS volumetric floods before they reach origin servers. Origin WordPress rate limiting provides granular application-level control based on WordPress User IDs and specific custom route logic.
Fail-open means that if your Redis cluster crashes or experiences network timeouts, the rate limiter automatically allows requests to pass through rather than returning 500 server errors, preserving business continuity.
Using the Token Bucket Redis hash structure (`HMSET` with 2 fields and TTL expiration), 100,000 active concurrent IP keys consume approximately 18MB to 24MB of Redis RAM.
Transients stored in the MySQL `wp_options` table should never be used for rate limiting because high-frequency SQL read/writes will cause severe table lock contention and crash MySQL under traffic spikes.
Primary references
Aditya Bhimrajka is a technology entrepreneur, product strategist, and software solutions expert with over a decade of experience building scalable web and mobile applications. His expertise spans SaaS, AI, cloud technologies, custom software development, and digital transformation. Passionate about solving real-world business challenges through technology, Aditya shares practical insights on WordPress, plugins, software development, startup growth, product strategy, and emerging technologies. At WPStack, he writes actionable, experience-driven content that helps developers, businesses, and website owners build secure, high-performing, and future-ready WordPress solutions.
Post a Comment